
Key Takeaways
- HTTP sends data as plain text; HTTPS encrypts it so third parties cannot read it in transit.
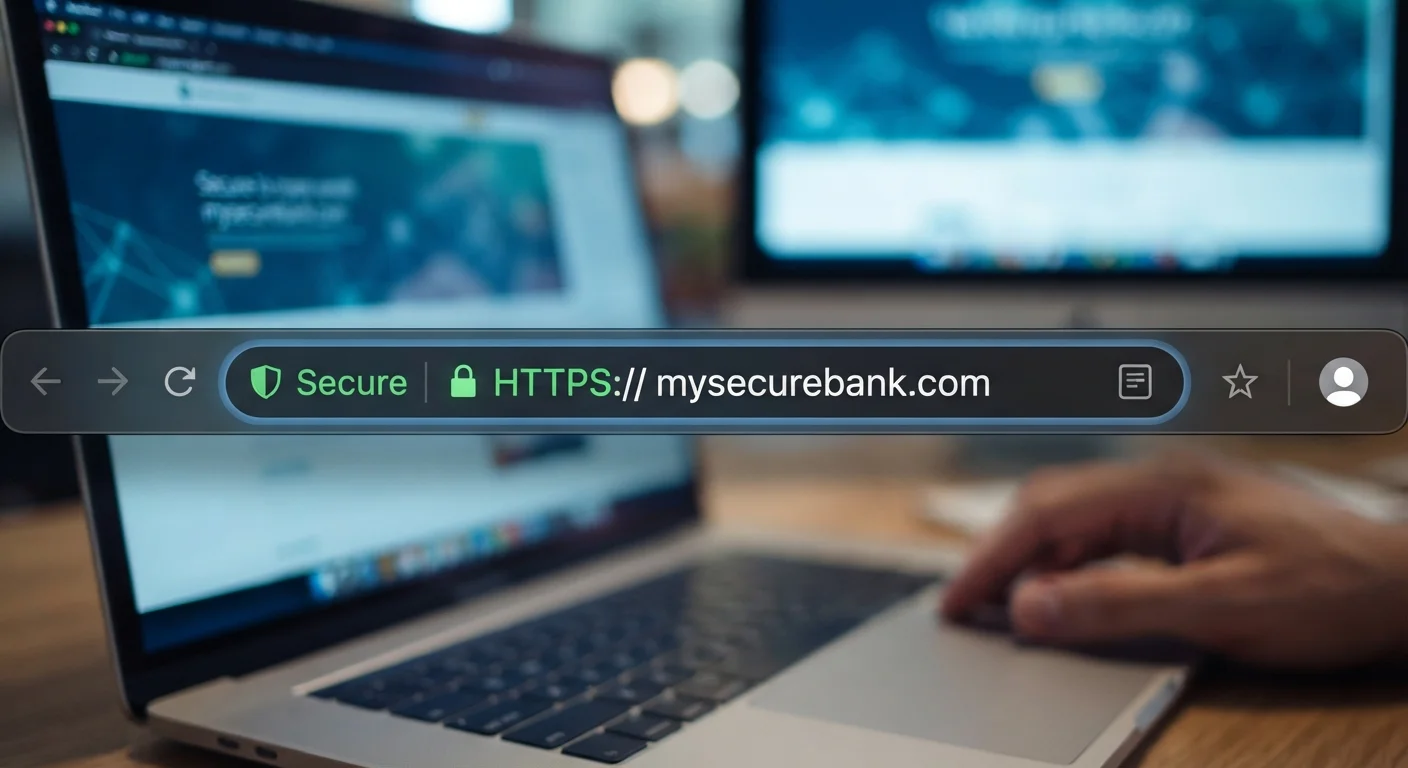
- The padlock icon in your browser bar confirms an active HTTPS connection using a valid certificate.
- On HTTP sites, anyone on the same network can potentially intercept what you send and receive.
- HTTPS does not guarantee a site is safe or trustworthy, only that the connection is encrypted.
- Most modern browsers now warn users when they land on an HTTP page.
Option A
HTTP
The original, unencrypted web protocol.
Best for: Viewing purely public content where no personal data is transmitted and privacy is not a concern.
Option B
HTTPS
The secure, encrypted standard for modern web browsing.
Best for: Any site where you log in, share personal details, make payments, or expect data privacy.
If you are logging into any account online
HTTPS
Credentials sent over HTTP are readable by anyone intercepting traffic on the same network. HTTPS encrypts the login exchange end-to-end.
If you are entering payment or billing information
HTTPS
Financial data transmitted over HTTP can be captured and read in transit. Only submit payment details on sites showing a valid HTTPS connection.
If you are reading a static public article with no login or forms
HTTP
The privacy risk is low for purely read-only public content, though most sites have migrated to HTTPS regardless for consistency and browser trust signals.
If you are browsing on public Wi-Fi
HTTPS
Public networks are easy to monitor. HTTPS protects what you send and receive even when the underlying network is untrusted.
What HTTP and HTTPS actually are
HTTP stands for HyperText Transfer Protocol. It is the set of rules that governs how data travels between your browser and a web server. When you type a web address and press Enter, your browser sends an HTTP request to a server, and the server sends back a response: the page you see.
HTTPS adds one critical layer to that process: encryption. The 'S' stands for Secure, and it means the connection is wrapped in a protocol called TLS (Transport Layer Security), formerly known as SSL. TLS scrambles the data in transit so that only your browser and the server can read it.
Think of HTTP as sending a postcard: anyone who handles it along the route can read what is written. HTTPS is closer to a sealed, tamper-evident envelope that only the recipient can open.
The padlock icon your browser displays is a visual shorthand for a confirmed TLS handshake. When you see it, your browser has verified that the server holds a valid certificate from a recognized Certificate Authority, and that the connection is encrypted.
The real risk of unencrypted connections
On an HTTP site, every piece of data you send or receive travels as plain text. That includes form fields, search queries, usernames, and passwords. Anyone positioned between your device and the server, whether on the same Wi-Fi network or further along the network path, can read that data with widely available tools.
This type of interception is called a man-in-the-middle attack. It is not a sophisticated exploit reserved for state-level actors. On an open public network, it requires only basic software and a few minutes of setup.
| Criterion | HTTP | HTTPS |
|---|---|---|
| Data in transit | Plain text, readable by third parties | Encrypted via TLS |
| Browser indicator | 'Not Secure' label or no padlock | Padlock icon in address bar |
| Certificate required | No | Yes, from a Certificate Authority |
| Susceptibility to interception | High, especially on shared networks | Low; encrypted channel |
| Safe for login/payment | No | Yes (channel only; verify the site) |
| Default on modern sites | Rarely used on maintained sites | Standard across the web |
HTTPS does not prevent every attack. A site can have a valid padlock and still host malicious content, use deceptive design, or collect your data in ways you did not expect. Encryption protects the channel, not the destination. For a broader picture of how sites track you beyond the connection itself, see how websites follow you through cookies and trackers.
If you browse over public Wi-Fi regularly, understanding what a VPN does and does not protect is worth your time alongside knowing the HTTPS basics.
How to read what your browser is telling you
Modern browsers have moved well past a simple padlock. Chrome, Firefox, Safari, and Edge each show connection status in the address bar, and their warnings have become more direct.
A padlock with no warning means the connection is encrypted and the certificate is valid. Clicking the padlock shows the certificate details: who issued it, what domain it covers, and when it expires.
A 'Not Secure' label before the URL means the page is using HTTP. Browsers started showing this label by default around 2018 as part of a broader push to normalize HTTPS across the web. Some browsers now block HTTP pages entirely on certain connections or require a click-through before displaying them.
A broken padlock or a red warning screen means the certificate is expired, does not match the domain, or was issued by an authority your browser does not recognize. These warnings should not be dismissed without a clear reason. A mismatched certificate can indicate a misconfigured server, but it can also indicate an active interception attempt.
For more on protecting your broader network environment, these home network security practices cover the steps most people skip.
Why HTTPS is now the baseline, not a bonus
For most of the web's history, HTTPS was used only on login pages and checkout flows. Running it required purchasing a certificate, which added cost and complexity. That changed significantly when the nonprofit Let's Encrypt launched in 2016, offering free, automated certificates. The barrier dropped, and adoption accelerated.
Google began using HTTPS as a ranking signal in search results around 2014, giving site operators another reason to migrate. By the early 2020s, the majority of web traffic was encrypted, according to data from Google's Transparency Report, which tracks the share of HTTPS page loads in Chrome.
For everyday browsing, this means you will rarely encounter a legitimate modern site that still runs on HTTP. When you do see one, it is a signal that the site has not been maintained, which may say something about its overall reliability.
It is also worth knowing that incognito mode does not change your connection protocol. An HTTP site is just as exposed in a private browsing window as in a regular one. What incognito mode actually prevents is a separate question from whether your connection is encrypted.