
Key Takeaways
- Social engineering targets psychology, not technology, making it effective against almost anyone.
- Phishing, pretexting, vishing, and baiting are the most common attack types.
- Attackers routinely use urgency and authority to pressure people into bypassing normal caution.
- Verifying the identity of anyone requesting sensitive information is the most reliable defence.
- No technical security tool fully replaces informed, sceptical human judgement.
Social engineering
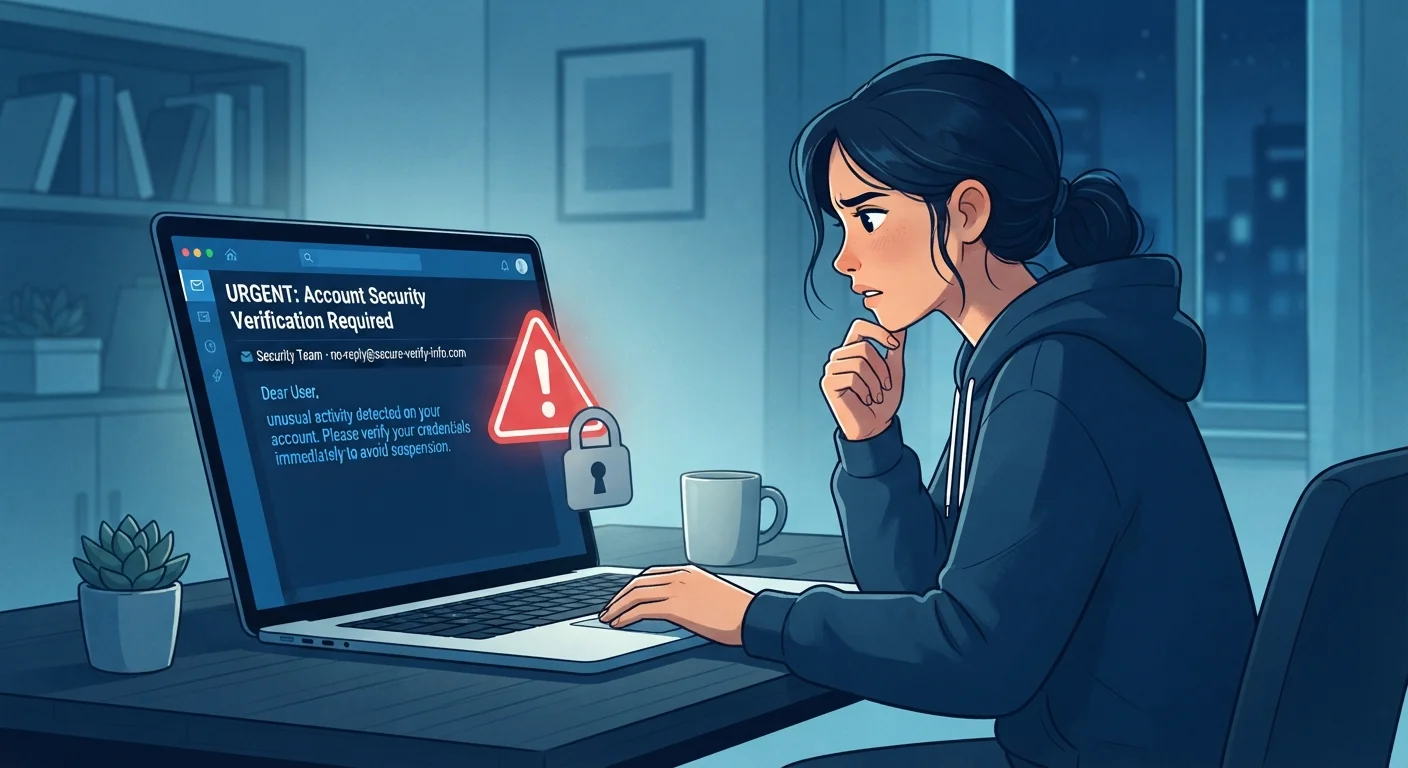
Social engineering is the practice of manipulating people into giving up sensitive information or taking actions that compromise security. Instead of hacking software or hardware, attackers exploit human psychology: trust, fear, urgency, and helpfulness. A social engineering attack might arrive as a fake email, a phone call from a supposed IT helpdesk, or a text message claiming your account is locked.
In cybersecurity, social engineering is classified as a non-technical attack vector, meaning it bypasses cryptographic or system-level defences entirely by targeting human decision-making.
Why attackers go after people instead of systems
Modern computer systems are hard to break into directly. Encryption, firewalls, and multi-factor authentication have raised the technical bar high enough that attackers frequently find it easier to bypass all of it by simply asking a person for access.
Human beings are wired to respond to authority, to help people who seem distressed, and to act fast when something feels urgent. Social engineers study these tendencies and design attacks around them. A well-crafted message that mimics your company's IT department, or a caller who convincingly poses as your bank's fraud team, can extract account credentials in minutes without touching a single line of code.
This is why even strong passwords leave gaps: the password itself is never the target. The person who holds it is.
Pause before you act on any urgent request
The most reliable defence against social engineering is a deliberate pause before responding to any message or call that creates urgency or asks for sensitive information. Ask yourself: would this organisation normally contact me this way? If anything feels off, verify through an official channel before doing anything else.
The main types of social engineering attacks
Attackers use several well-documented techniques, often combining more than one in a single attempt.
- Phishing: Fraudulent emails designed to look legitimate, typically asking the recipient to click a link or enter credentials on a fake site. Spear phishing personalises the message using details gathered from social media or company websites.
- Vishing: Voice phishing over the phone. A caller impersonates a trusted figure and uses conversation to extract information in real time.
- Smishing: The same approach delivered by SMS. Messages about failed deliveries, overdue accounts, or prize claims are common formats.
- Pretexting: The attacker constructs a believable scenario (a pretext) to justify their request. An example is someone calling a company and claiming to be an auditor who needs employee payroll data.
- Baiting: Leaving a USB drive in a parking lot or office lobby, labelled to look interesting. Curiosity leads someone to plug it in, installing malware automatically.
- Tailgating: Physical access to a building by following an authorised employee through a secure door, relying on politeness to avoid challenge.
Each method works because it mimics a normal, legitimate interaction closely enough that the target does not pause to question it.
74%
Of data breaches involve a human element
According to Verizon's 2023 Data Breach Investigations Report, the majority of confirmed breaches involve human factors including social engineering, errors, and misuse.
3.4 billion
Phishing emails sent daily
Cybersecurity researchers estimate this volume of phishing messages is sent globally each day, making it the single most common form of social engineering.
60 seconds
Median time before a phishing link is clicked
The Verizon 2023 DBIR found that half of phishing email recipients who click do so within the first minute of receiving the message, before scepticism has time to engage.
The psychological levers attackers use
Social engineering is applied psychology. Researchers studying deception and persuasion have identified a consistent set of triggers that attackers exploit.
Urgency is the most common tool. A message warning that your account will be suspended in 24 hours compresses your thinking and makes you less likely to stop and verify the source. Authority works similarly: a request that appears to come from a CEO, a government agency, or a bank carries weight that bypasses normal scepticism. Scarcity and fear follow the same pattern, as does reciprocity, where an attacker provides something small (a piece of useful information, a favour) before making a request.
Helpfulness is also exploited. Most people want to assist a colleague who seems stuck or a caller who sounds genuinely worried. Attackers position themselves as people in need of a small favour that turns out to be a password or access code.
Understanding these levers does not make you immune, but it creates a moment of pause. That pause is often enough to catch an attack before it succeeds. A solid grounding in online privacy basics makes these patterns easier to spot.
Practical ways to reduce your exposure
No single habit eliminates social engineering risk, but several practices together make attacks significantly harder to pull off.
Verify before you act. If a message or call requests sensitive information, hang up or close the message and contact the organisation directly using contact details from their official website. Do not use a phone number or link provided in the suspicious communication itself.
Slow down on urgent requests. Artificial urgency is a primary warning sign. Legitimate banks and government agencies do not demand immediate action under threat of account closure or legal consequences.
Share less publicly. Attackers research targets before making contact. The less detail about your employer, role, or personal schedule is publicly visible, the harder it is to craft a convincing pretext. Review your social media visibility settings periodically. The personal privacy audit checklist covers this step systematically.
Question unusual requests. If a colleague emails asking for a wire transfer or a password reset in an unusual way, call them directly to confirm. Compromised email accounts are a common tool for internal phishing.
Combining these habits with the security practices for your home network closes many of the gaps that attackers commonly target.